Prove your AI
can be trusted.
Deploy AI with confidence through machine-verifiable trust, continuous assurance, and audit-ready governance.
Sentrify is the independent trust layer that evaluates, certifies, and monitors AI agents before and during deployment.
ISO 42001 Aligned · 94 controls · AWS Sydney residency
AI is moving faster than trust
Organisations are deploying AI into critical decisions — credit scoring, hiring, patient triage, and citizen services. But the processes for proving those systems are safe, fair, and compliant remain manual, fragmented, and dangerously slow.
"You can deploy AI in days. Proving it's safe, compliant, and trustworthy? That takes months."
Manual Governance
Spreadsheets, committees, and document trails that don't scale
Regulatory Exposure
Regulators like APRA, ASIC, AER, and TEQSA demand evidence you don't have
No Proof Layer
Assessments exist; verifiable, traceable assurance aligned to frameworks such as ISO 42001, the EU AI Act, and Aus Government AI Safety Standards does not
Introducing Sentrify for measurable AI trust
Sentrify transforms AI governance from a manual, reactive process into a continuous, automated trust layer. Instead of documents, checklists, and committees — you get machine-verifiable trust with full traceability, from first registration to continuous post-deployment monitoring.
This is not just governance software. This is the trust layer that makes AI deployment safe to say yes to.
Four core layers. Eight integrated modules. One trust platform.
AI Registry & Inventory
See every AI system. Know every risk.
Register AI systems and agents across your organisation, capture ownership, use cases, and risk context, and maintain full lifecycle visibility from inception to decommissioning.
Learn more →Evidence & Trust Layer
Turn governance into verifiable proof.
The Evidence Hub stores, versions, and integrity-hashes all governance artefacts — linking policies, controls, and documentation to specific AI systems with a confidence index based on completeness.
Learn more →Automated Evaluation Engine
Test trust. Automatically.
Rule-based and LLM-assisted evaluation runs security, bias, and governance checks across your AI systems. Framework-aligned evaluation packs mean you test against the standards that matter to your regulators.
Learn more →TrustScore™
The universal metric for AI trust.
A deterministic, pillar-weighted scoring engine that produces a single, auditable TrustScore (0–100) for every AI system — enabling risk-tier classification and deployment decision support.
Learn more →From registration to
trusted deployment — in one platform
Six steps. Fully automated. Audit trail at every stage.
Register AI
Capture the AI system, its purpose, the data it uses, who owns it, and its initial risk classification.
Upload Evidence
Attach governance documentation, policies, bias assessments, security controls, and vendor records.
Run Evaluation
Run the five-phase evaluation: risk scoring, test plan and control evaluation. Every control is assessed through four layers: rules, LLM-assisted reasoning, evidence validity and adversarial probe packs.
Get TrustScore
Phase 4 of 5. Receive a deterministic TrustScore with a full pillar-by-pillar breakdown and risk-tier classification.
Generate Assurance Report
Phase 5 of 5. Produce an audit-ready assurance report with full evidence chain and traceability metadata.
Monitor Continuously
As the AI system evolves, Sentrify re-evaluates and updates the TrustScore — trust is never assumed, always proven.
From committees to continuous governance
Replace static governance models — endless meetings, disconnected sign-offs, and document-based audit trails — with structured, automated governance workflows. Approval pipelines. Ethics review stages. Role-based decisioning. All in one platform.
| Role | Capability |
|---|---|
| Admin | Full governance control — configure frameworks, manage users, set organisational risk thresholds |
| Manager | Evaluation ownership and approval — run assessments, trigger reviews, approve AI for deployment |
| User | Read access and reporting — view TrustScore™ results, download reports, track status |
| Auditor | Independent verification — access full evidence chains, immutable audit logs, assurance certificates |
Sentrify operates the service through a separate internal Platform Admin role, which is not a customer role.
Your industry. Your compliance requirements. One platform.
Every standard
that matters.
Sentrify's evaluation engine maps directly to the frameworks your regulators, boards, and auditors care about.
Applicable across regulated industries
Built as infrastructure. Not bolted on.
Sentrify sits between your AI systems and the decisions those systems power. It's not a dashboard on top of your stack — it's the trust layer underneath it.
Input
Sentrify Trust Layer
Output
Assurance you can defend.
Built for regulators and auditors, not just dashboards. Every score, every decision, every document — traceable, reproducible, and defensible.
Deterministic TrustScore™
Pure math — zero LLM in the scoring path. Every score is pillar-weighted, fully reproducible, and traceable to the exact control results that produced it.
Engine + versioned assurance packs
A domain-neutral evaluation engine paired with framework packs that are versioned and immutable once published. Every evaluation references the exact pack version it ran against — no ambiguity when standards change.
"What to Test" generator
An AI-recommended test plan generated from each system's risk profile before evaluation starts. Teams know exactly what to evaluate — no guesswork, no blank-page planning.
Adversarial testing built in
Versioned adversarial probe packs are bound to controls and executed as a fourth evaluation layer — structured red-teaming that produces a traceable, pack-versioned record alongside the control evaluation.
Immutable evidence chain
SHA-256-keyed evidence content, integrity-hashed evaluation reports, and append-only audit logs. Built from the ground up to survive regulatory review and legal scrutiny.
The Sentrify difference
| Traditional GRC | Generic AI Governance | Sentrify |
|---|---|---|
| Manual processes | Surface-level checks | Continuous automated assurance |
| Static, point-in-time | No audit traceability | Full evidence chain with integrity hashing |
| Not AI-aware | No deterministic scoring | TrustScore™ — transparent, auditable |
| Governance as paperwork | One-size-fits-all | Framework-native, industry-specific |
| Slow to respond to change | No lifecycle monitoring | Continuous re-evaluation as AI evolves |
Notes on Responsible AI
Practitioner perspectives on AI governance, audit-ready evidence, and the regulatory landscape shaping enterprise AI.




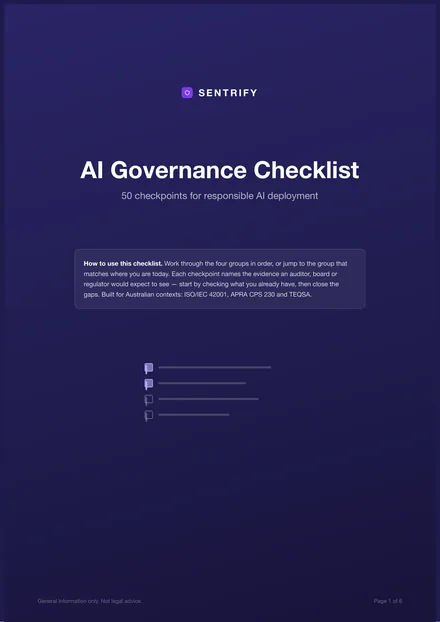
AI Governance Checklist
50 checkpoints for responsible AI deployment: governance documentation, evidence requirements, control mapping and regulator-ready reporting. Built for Australian compliance contexts (ISO 42001, APRA CPS 230, TEQSA).
Questions, answered.
TrustScore™ is a deterministic 0–100 governance-posture score produced after control evaluation. It is computed from control results using pillar-weighted math — no LLM is involved in the scoring path. Every score is fully auditable and reproducible, pillar by pillar.
Don't deploy AI
without trust.
Every AI system you deploy carries risk. Sentrify makes that risk visible, measurable, and manageable — before deployment, and continuously afterwards.
No commitment required. See Sentrify evaluate a real AI system in a 30-minute demo.